COHORT 01 · SEPTEMBER 2026

ETHICAL HACKING COURSE

From the first command to compromising an entire system

In 40 weeks you'll learn to think like an attacker — and like a professional pentester. You won't watch videos: you hack in a real lab, on real targets, alongside a mentor.

40Weeks of training
33Modules
4Complex labs
16Maximum group size
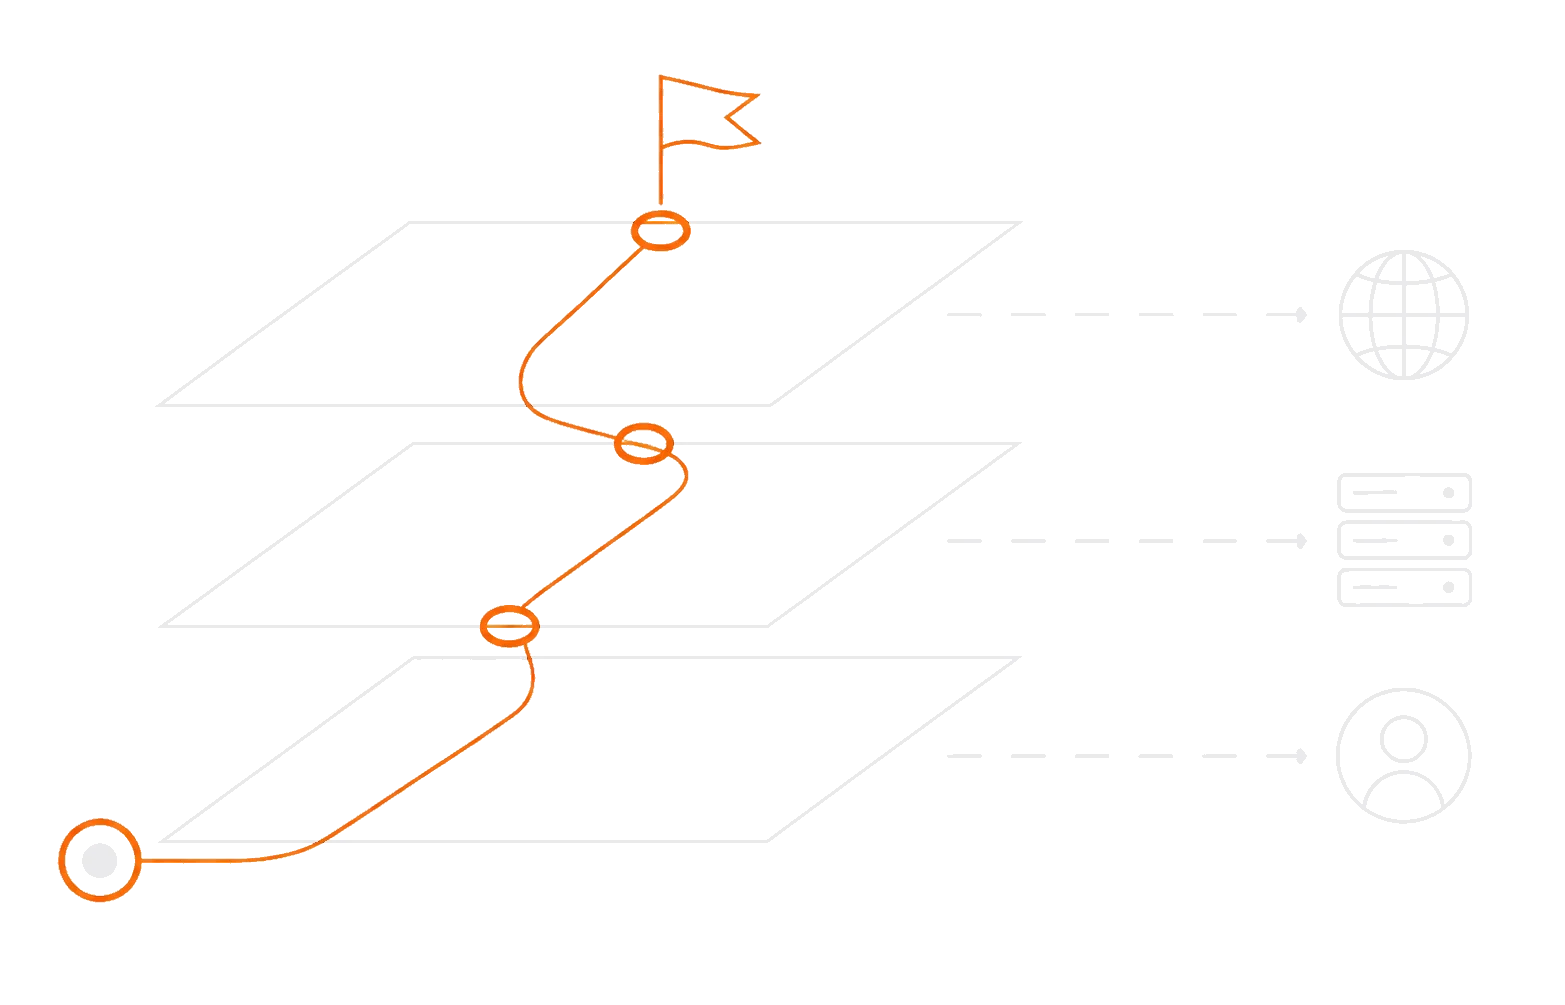
A tanulási út: az alapoktól a haladó szintig, három egymásra épülő rétegen keresztül

Not videos.
A real classroom,
real tools and
real tasks.

A hands-on ethical hacking course where you learn with real tools on real vulnerabilities — in a controlled environment, in the same room as your instructors. The goal isn't a certificate, but market-ready skills.

Reserve your seat

Send us your details and we'll get in touch.

Briefly tell us where you're starting from and why the course interests you.
Matek Kamilló, etikus hacker és security researcher Kamilló avatarja

Instructor

Matek Kamilló

Ethical hacker and security researcher

Matek Kamilló specializes in the deep technical security assessment of complex IT systems. His work goes beyond traditional penetration testing: his key areas are offensive security, red teaming, reverse engineering and exploit development.

His research has earned him more than 15 publicly registered CVEs, including critical vulnerabilities identified in widely used technology and security products.

His qualifications — which can't be bought, only earned with knowledge and dedication
KCEHOSCPOSWEOSWPARTE · AWS Red Team Expert
"A locksmith can use their skills to help with a damaged door, but also to commit a crime." — according to Kamilló, hacking works the same way. On this course you learn how to use it for good and legal purposes — professionally.
— Curriculum

40 weeks — from the first command to compromising an entire system

Four stages that build on each other, with clear outcomes. By the end you'll have compromised real targets, alongside a mentor.

The learning path · Stage 1–2

Fundamentals and the web attack surface

01

~/tanrend/01_alapok

01 / 04

Foundations you can build on

An attacker doesn't learn tricks — they understand how systems work.

•Linux under the hood — command line, permissions, processes
•Networking and TCP/IP — so you see and understand what travels on the wire
•Wireshark, tcpdump, nmap, netcat — the pentester's core tools
•Target reconnaissance and OSINT — what a company reveals without knowing it
✓By the end of the stage: you independently map an unknown network and know exactly what services run on it.
02

~/tanrend/02_web_api

02 / 04

Web & API — where most gaps are

The vast majority of attacks start here — from the classics to the modern API world.

•XSS, proxy-based analysis — manipulating HTTP traffic
•SQL injection — how an entire database leaks out
•Auth and session flaws — hijacked accounts, bypassed login
•Breaking REST and GraphQL APIs — the weak point of today's systems
•Attack chain — combining multiple vulnerabilities into a single breach
✓By the end of the stage: you compromise a vulnerable web application and reach the database through chained flaws.
The learning path · Stage 3–4

Beyond the web, and the corporate internal network

03

~/tanrend/03_wifi_mobil_iot

03 / 04

Beyond the web — wireless, mobile, IoT

We step out of the browser into the physical and embedded world, where different rules apply.

•WiFi from the inside — sniffing, attacks against WPA2
•Evil Twin and war driving — fake networks, real victims
•Hacking mobile and IoT devices — with live practice
•Windows and Linux exploits — attacking the heart of the system, by hand
✓By the end of the stage: you break into a WiFi network and take control of a target machine with a successful exploit.
04

~/tanrend/04_ad_belso_halozat

04 / 04

The big game — internal network and AD

This is where someone becomes a real pentester — we put companies' most guarded systems to the test.

•Active Directory — structure and weak points
•Internal recon, credential harvesting — collecting passwords
•Pass-the-hash and Kerberos attacks — in practice
•Lateral movement and privesc — on the way to domain admin
•Pivoting, tunneling, social engineering — and professional reporting
✓By the end of the stage: from a single initial foothold you take control of an entire corporate domain — and document how in a professional report.
— FAQ

Frequently asked questions about the course

We've tried to answer every important question, but if anything is still unclear, don't hesitate to reach out.

+Do I need prior professional experience?
It's not a requirement. Basic computer and networking knowledge is an advantage, but the course starts from the fundamentals, and thanks to the small group everyone progresses at their own pace — the motivated beginner and the more experienced IT professional alike.
+Can it be completed online?
No. The course runs exclusively in person, in a hands-on format, because ethical hacking can only truly be learned through real tasks in live labs — not from pre-recorded videos.
+What does the admission interview involve?
Applying doesn't mean automatic admission: we hold a personal admission interview with every applicant. It focuses not on prior professional experience but on motivation and an ethical mindset.
+Do you accept corporate applicants?
Yes. An organization can delegate several employees to the open course. Beyond that — independently of this course — we also run closed, group training for companies by separate agreement, tailored to the team's needs and goals. Note your interest on the application form, or get in touch with us.
Contact →
— The outcome

Market-ready skills, not just a certificate

The goal isn't the paper itself, but that by the end of the course you leave with the practical skills the job market actually needs.

No one can responsibly promise a guaranteed job or salary — we work for usable knowledge, and we embed it in practice.

  • Attacker mindset for effective defense.
  • Vulnerability assessment and practical knowledge of pentest fundamentals.
  • Tooling in a real, controlled lab environment.
  • Reporting and formulating hardening recommendations.

Reserve your seat.

The first cohort starts soon, in September 2026.

Participation is limited to just 16 seats. The course requires an admission interview; applying doesn't mean automatic admission. In the interview we focus not on prior experience but on an ethical mindset.

Apply →